Author: DEROBS

  • Enhancing fire safety in lithium-ion battery energy storage systems

    Enhancing fire safety in lithium-ion battery energy storage systems

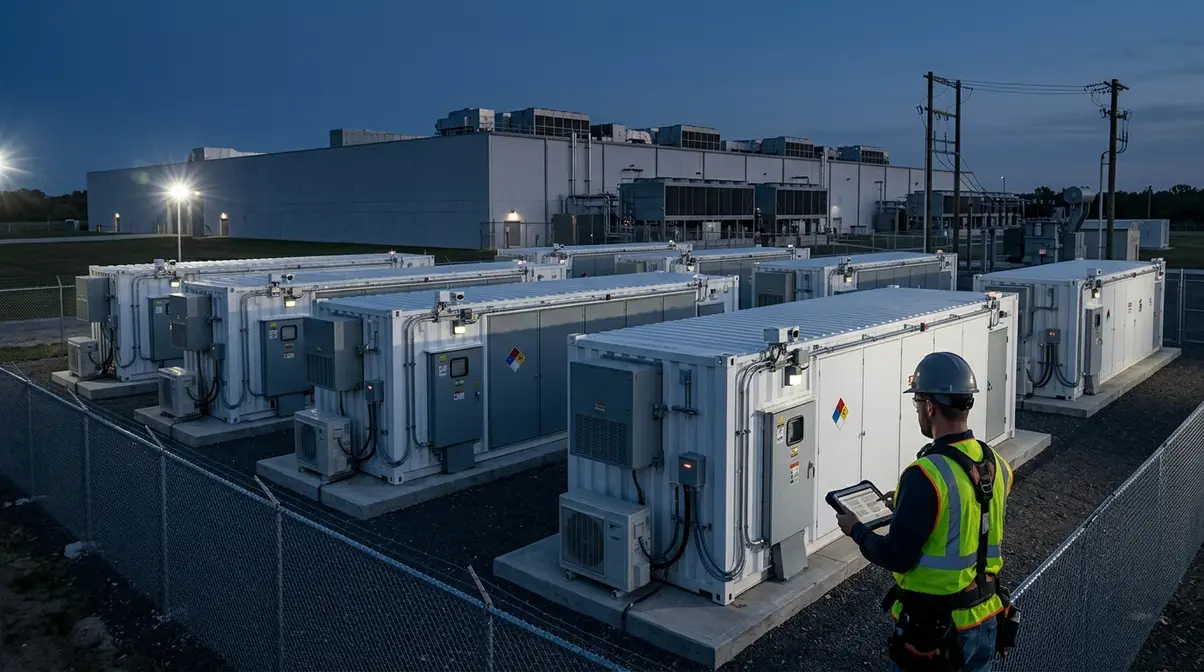
    <p>As the deployment of lithium-ion battery energy storage systems (BESS) scales to support digital infrastructure, fire safety remains a primary concern for operators. Recent industry guidance highlights how updated safety standards and the integration of early off-gas detection technologies are essential for maintaining operational compliance and protecting physical assets.</p><p>A critical focus in modern BESS safety is the prevention of thermal runaway—a condition where a cell enters an uncontrollable, self-heating state. Industry experts emphasize that early detection of off-gassing, which occurs before a visible fire or explosion, provides a vital window for intervention. By identifying these chemical precursors, site operators can initiate safety protocols to mitigate risks before a system failure escalates.</p><p>Adherence to evolving fire safety standards is increasingly necessary for regulatory compliance and risk management. These standards outline the technical requirements for site design, monitoring, and emergency response, providing a framework for operators to navigate the safety complexities of large-scale battery deployments.</p><p>For the digital economy, where reliable power is non-negotiable, integrating these advanced detection systems is becoming a best practice for digital infrastructure projects. Ensuring compliance with current safety benchmarks helps organizations safeguard their continuity while meeting increasingly stringent industry mandates.</p>

    Source: Data Center Dynamics
    Original article: https://www.datacenterdynamics.com/en/whitepapers/the-ultimate-guide-to-li-ion-bess-fire-safety-standards/
  • Figma co-founder discusses limitations of Model Context Protocol

    Figma co-founder discusses limitations of Model Context Protocol

    <p>Figma co-founder Dylan Field recently commented on the Model Context Protocol (MCP), suggesting that the technology is not a perfect solution for all data integration needs. The discussion centers on the challenges of balancing industry-standard interoperability with the necessity of protecting sensitive user data.</p><p>Figma has stated that it aims to support as many technical standards as possible to foster integration and utility. However, the company emphasized that this commitment is qualified by its security posture, noting that it will not expose all of its internal data to satisfy the requirements of a single protocol.</p><p>The remarks highlight the ongoing industry challenge of implementing standardized interfaces for AI models without compromising the privacy and integrity of enterprise-level platforms.</p>

    Source: TechCrunch
    Original article: https://techcrunch.com/2026/10/20/figma-co-founder-dylan-field-thinks-mcp-is-not-a-perfect-protocol/

  • UK competition watchdog proposes opening iPhone contactless payments

    UK competition watchdog proposes opening iPhone contactless payments

    <p>The United Kingdom's competition regulator has launched a formal consultation regarding proposals to grant third-party providers access to iPhone contactless payment technology. The initiative is intended to foster greater competition within the digital payments sector by enabling alternative services to operate more effectively on Apple devices.</p><p>By opening up access to this near-field communication (NFC) hardware, the regulator aims to remove existing technical barriers that currently favor Apple's proprietary payment system. The proposal is also designed to lower costs for businesses and consumers by encouraging a more competitive landscape for payment processors and digital wallets.</p><p>The move represents a significant regulatory step in addressing the dominance of integrated mobile payment ecosystems. The outcome of this consultation process will determine the next steps in potentially mandating broader accessibility for rival payment technologies on iPhones within the UK market.</p>

    Source: Finextra
    Original article: https://www.finextra.com/newsarticle/48618/uk-sets-out-proposal-to-open-up-access-to-iphone-contactless-payments?utm_medium=rssfinextra&utm_source=finextrafeed

  • Addressing the workforce challenge in the data center industry

    Addressing the workforce challenge in the data center industry

    <p>In a recent episode of DCD Studio, Andy Davis of Data eXec joined Seb Moss to discuss the evolving human capital requirements of the data center sector. As the industry undergoes a period of rapid growth, the pressure to maintain a high-quality, sustainable, and diverse workforce has become a primary operational priority.</p><p>The discussion emphasized that successful talent acquisition and retention in the data center space require more than traditional hiring methods. Organizations are increasingly tasked with developing inclusive corporate cultures that can attract a broader pool of talent to meet the sophisticated technical demands of modern infrastructure.</p><p>Davis highlighted that building an inclusive and sustainable culture is essential for navigating the current industry expansion. By prioritizing these elements, firms aim to better manage the challenges associated with scaling operations and ensuring long-term staff stability in a highly competitive market.</p>

    Source: Data Center Dynamics
    Original article: https://www.datacenterdynamics.com/en/videos/dcd-studio-the-data-center-workforce-challenge-with-andy-davis-data-exec/

  • DHS mandates removal of DeepSeek products across federal civilian agencies

    DHS mandates removal of DeepSeek products across federal civilian agencies

    <p>The U.S. Department of Homeland Security (DHS) has issued a formal directive ordering federal civilian agencies to cease the use of DeepSeek products. Under this new mandate, agencies are required to identify and remove all instances of DeepSeek software or services from government systems.</p><p>This directive reflects an ongoing effort by U.S. regulatory bodies to secure federal infrastructure against potential risks associated with foreign-developed software. The move effectively bars the deployment of these AI products within the federal civilian space.</p><p>The DHS action serves as an administrative control measure aimed at protecting sensitive government data and maintaining the integrity of digital infrastructure. Further details regarding the implementation timeline or specific remediation steps for agencies have not been publicly elaborated beyond the initial order to cease use and remove the technology.</p>

    Source: BleepingComputer
    Original article: https://www.bleepingcomputer.com/news/security/dhs-bans-deepseek-products-across-us-federal-civilian-agencies/

  • Hackers exploit AI penetration testing tool Cairn in widespread attack campaign

    Hackers exploit AI penetration testing tool Cairn in widespread attack campaign

    <p>Cybersecurity reports indicate that a Chinese-speaking threat actor is actively abusing Cairn, an AI-powered penetration testing tool, to conduct a large-scale series of cyberattacks. The campaign has resulted in the compromise of hundreds of websites across the globe.</p><p>The scope of the attacks has targeted several prominent organizations, including agricultural machinery leader John Deere, consumer product developer SharkNinja, and engine manufacturer Cummins. By utilizing an automated tool originally designed for security assessment and penetration testing, the attacker has successfully scaled their operations to infiltrate numerous targets.</p><p>The incident highlights growing concerns regarding the dual-use nature of artificial intelligence in cybersecurity. While tools like Cairn are developed to assist security professionals in identifying vulnerabilities, their automation capabilities can be repurposed by malicious actors to expedite reconnaissance and exploitation phases of an attack.</p><p>As of this reporting, the specific technical mechanisms through which the attacker is weaponizing the tool remain under investigation. The scale of the breach underscores the risks associated with the proliferation of AI-assisted offensive security technologies and the ongoing challenge for enterprises to defend against automated, intelligent threats.</p>

    Source: Dark Reading
    Original article: https://www.darkreading.com/cyberattacks-data-breaches/hackers-abuse-ai-pen-test-tool-cairn

  • Developer proposes conversion of hotel basement into Lancashire data center

    Developer proposes conversion of hotel basement into Lancashire data center

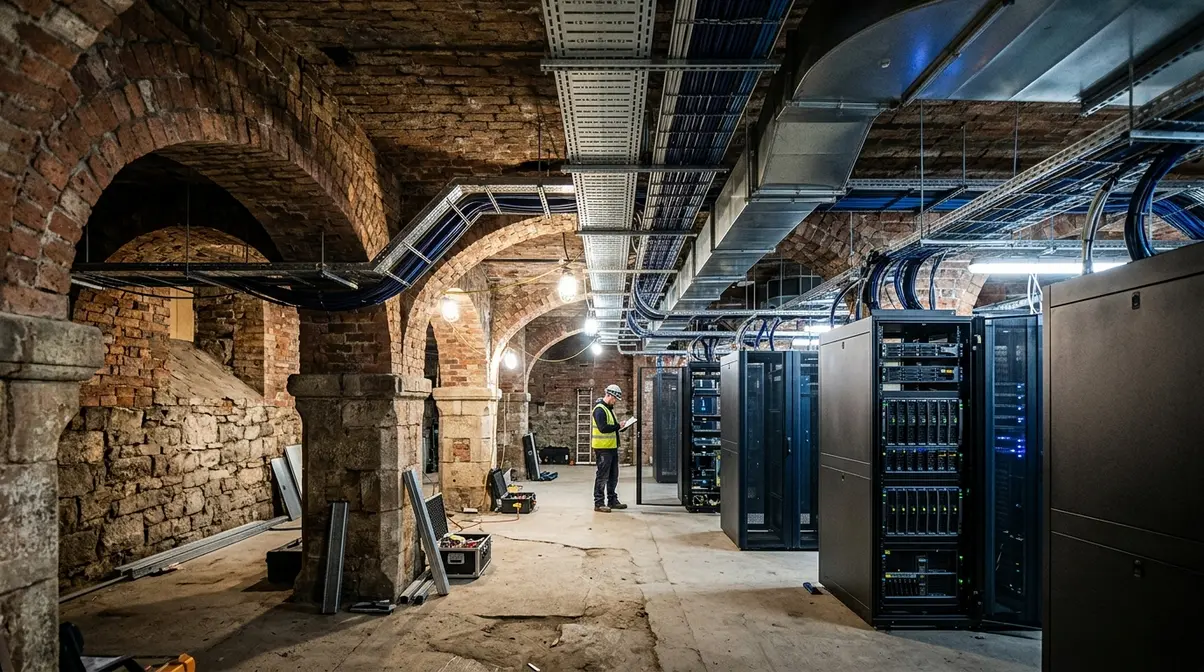
    <p>A development project in Lancashire, UK, seeks to repurpose the basement of a 66-year-old hotel into a data center facility. The proposed site, characterized by its age and current hospitality use, is slated for a structural renovation to accommodate the requirements of digital infrastructure.</p><p>As the demand for localized computing capacity grows, developers are increasingly exploring adaptive reuse projects for existing structures. While the conversion of older buildings presents unique logistical and structural challenges, such projects reflect broader trends in the densification of digital infrastructure within established urban and semi-urban environments.</p><p>Further details regarding the project's technical specifications, timeline, or planning approvals were not immediately available beyond the reported intent to utilize the basement space for data operations.</p>

    Source: Data Center Dynamics
    Original article: https://www.datacenterdynamics.com/en/news/developer-looks-to-convert-hotel-basement-into-data-center-in-lancashire-uk/

  • Sustainable Finance Live 2026 opens in London

    Sustainable Finance Live 2026 opens in London

    <p>The Sustainable Finance Live 2026 conference has officially commenced in London. The event opened with a keynote address delivered by Richard Peers, the founder of ResponsibleRisk and a contributing editor at Finextra.</p><p>The conference focuses on the intersection of banking and community development, exploring the role financial institutions play in supporting local economic stability and sustainability.</p>

    Source: Finextra
    Original article: https://www.finextra.com/newsarticle/48611/sustainable-finance-live-2026-why-banks-should-prioritise-investing-in-thriving-communities?utm_medium=rssfinextra&utm_source=finextrafeed

  • Symbiosis Coalition commits to 320,000-ton carbon removal deal with Working Trees

    Symbiosis Coalition commits to 320,000-ton carbon removal deal with Working Trees

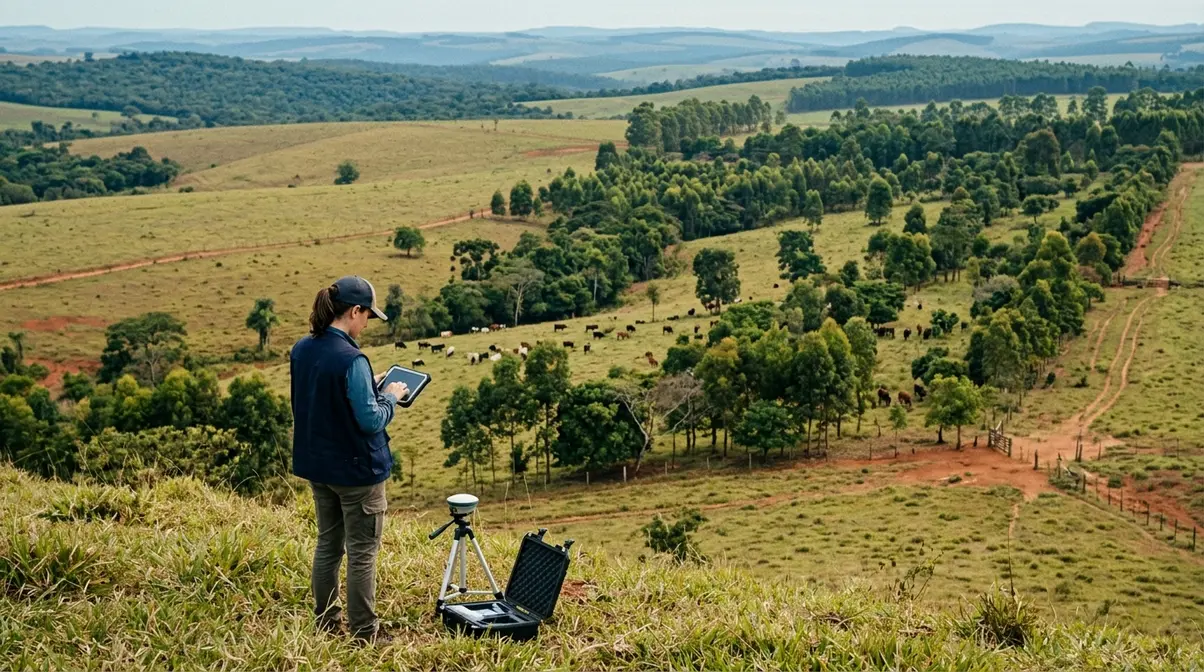
    <p>The Symbiosis Coalition, a group backed by Google, has announced a new carbon removal agreement with the agroforestry company Working Trees. The deal involves the removal of 320,000 tons of carbon.</p><p>The project focuses on restoring environmental health by converting degraded cattle pastures in Brazil into mixed-species silvopasture systems. This approach integrates trees into livestock farming areas, which can improve soil health and increase carbon sequestration compared to traditional grazing methods.</p>

    Source: Data Center Dynamics
    Original article: https://www.datacenterdynamics.com/en/news/google-backed-symbiosis-coalition-signs-320000-ton-carbon-removal-deal-with-agroforestry-firm-working-trees/

  • Enersense and Betolar join forces to develop security solutions for Baltic infrastructure

    Enersense and Betolar join forces to develop security solutions for Baltic infrastructure

    <p>Finnish companies Enersense and Betolar Oyj have announced a partnership aimed at developing security solutions for critical infrastructure, including electrical substations and data centers. The initiative will focus on deploying these solutions across the Baltic region.</p><p>The collaboration targets grid and industrial customers, addressing the growing need for enhanced security measures for vital digital and energy assets. By leveraging their respective expertise, the two firms intend to provide specialized protective infrastructure tailored to the operational demands of the Baltic market.</p><p>Further technical specifications and project timelines have not been publicly detailed at this stage.</p>

    Source: Data Center Dynamics
    Original article: https://www.datacenterdynamics.com/en/news/enersense-and-betolar-oyj-to-develop-security-solutions-for-substations-and-data-centers-across-the-baltics/